

Six things the platform does.
See what data you have, know what is in it, know who can reach it, find the permissions that are quietly broken, stop what should not be happening, and put back exactly what was hit. One appliance, two packages.

Syslog CEF and REST, into the tool you already run

The one everybody has.
Broken permissions
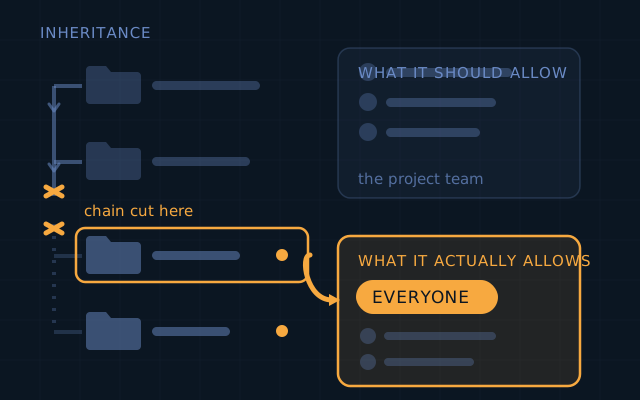
Every file estate accumulates them: a folder cut loose from its inheritance, a person granted access directly instead of through a group, an entry for an account that was deleted three years ago. None of it shows up in a group review, none of it triggers an alert, and all of it is still live. It is the single most common finding when we first scan a landscape — and the one that turns a single compromised account into a company-wide incident.
- Broken inheritance
- Direct permissions on files
- Orphaned SIDs
- Everyone and Domain Users
- Nested group loops
- Stale and disabled accounts
Pick the one you came for.

Data visibility
Every file operation recorded, plus the capacity reports that answer the weekly questions.

Classification
Personal, health and financial data found in the files themselves, on your own hardware.

Access analytics
Effective permissions through every nested group, ranked by what is behind them.

Ransomware containment
The responsible account blocked in seconds. Everyone else keeps working.

Rapid recovery
Single-file restore scoped to the damage, from the snapshots you already take.

Broken permissions
Inheritance cut, direct grants, orphaned SIDs and open shares — ranked by what sits behind them.
Let’s solve your data challenges.
Connect with our engineers to find the right approach for your infrastructure.
Which package has what.
DataGovernance contains everything in DataDefense. The difference is what it adds on top.
ProLion DataDefense
See your data, and stop what should not be happening to it.
Visibility, containment and recovery.
ProLion DataGovernance
Everything in DataDefense, plus the answer to who can reach what.
Everything above, and then some.
Wherever your data already sits.
Each system is read through its own native interface — FPolicy on NetApp ONTAP, CEE on Dell, the ProLion Security Service on Windows Server, and the Microsoft 365 audit log and APIs for SharePoint Online and OneDrive. Lightweight collectors sit in each data center. Nothing is installed on endpoints, and everything runs on your own hardware, including at dark sites.
Talk to an engineer who knows your data.
Four fields, and somebody who knows ONTAP, PowerScale and what FPolicy does. Not a qualification call.