31 Dec 2026

Varonis is pulling the plug on on-prem. ProLion isn’t.

Learn how to keep your data →
For security teams
Industries
Healthcare

Your Most Sensitive Data Is On-Prem. So Is Your Biggest Blind Spot.

ProLion shows you what’s there, who’s touching it, and what’s at risk, in real time, without your data ever leaving your environment.
Splunk
Microsoft Sentinel
Elastic
IBM QRadar

Syslog CEF and REST, into the tool you already run

One day of alerts. One of them mattered.

Nearly half of what reaches the queue is a false positive, and a good share is never looked at. Adding another noisy source does not help. Adding the one tier nobody covers does.
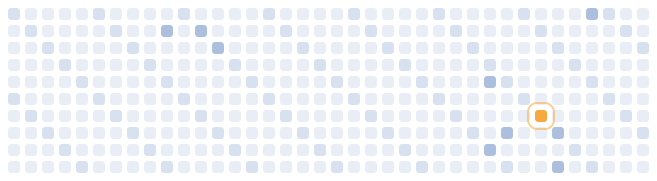
A day of alerts drawn as small squares; one square, a mass rename on a file share at 03:00, is highlighted.
Alerts in the queueInvestigatedA mass rename on a file share, 03:00
46 %
of alerts turn out to be false positives.
Half
of alerts are never investigated at all.
78 %
of analysts need ten minutes or more per alert.

Industry figures, not ProLion measurements. Sources: Microsoft and Omdia, State of the SOC 2026; Vectra AI 2026; CriticalStart analyst survey.

See it running

Watch the one alert that mattered.

1:01

Let’s solve your data challenges.

Connect with our engineers to find the right approach for your infrastructure.

Why the file layer is the tier that is missing.

Valid credentials look normal
To a firewall and to an endpoint tool, an attacker who signed in is a user. On the file layer they stop looking normal immediately.
Behavior, not signatures
A mass rename at 03:00 by an account that reads twelve files a day is caught on shape, not on a pattern someone published.
Containment, not a ticket
The account is cut off from the data in seconds. The alert arrives afterward, with the action already taken.
Exposure you can quantify
How many sensitive files are reachable by how many people — a number for the board, and one you can shrink.
Proof that it stayed shrunk
Every ACL and ownership change, recorded as it happens.
In your tools, not another console
Syslog CEF and REST into Splunk, Sentinel, QRadar and Elastic; blocking and quarantine from your playbooks.

What lands in your SIEM.

Not “something happened on the file server”. The account, the path, the rule and what was already done about it.

ProLion · ransomware pattern03:00:12
Account
CORP\m.reiter
Host
svm-fileserv-02
Path
\\fs02\engineering\projects\2026\*
Rule
Mass rename · behavior off baseline
Files touched
1,284
Action
User blocked · 4 s after first event

An example event, for illustration.

Talk to an engineer who knows your data.

Four fields, and somebody who knows ONTAP, PowerScale and what FPolicy does. Not a qualification call.

Four fields. No hidden newsletter.

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.