
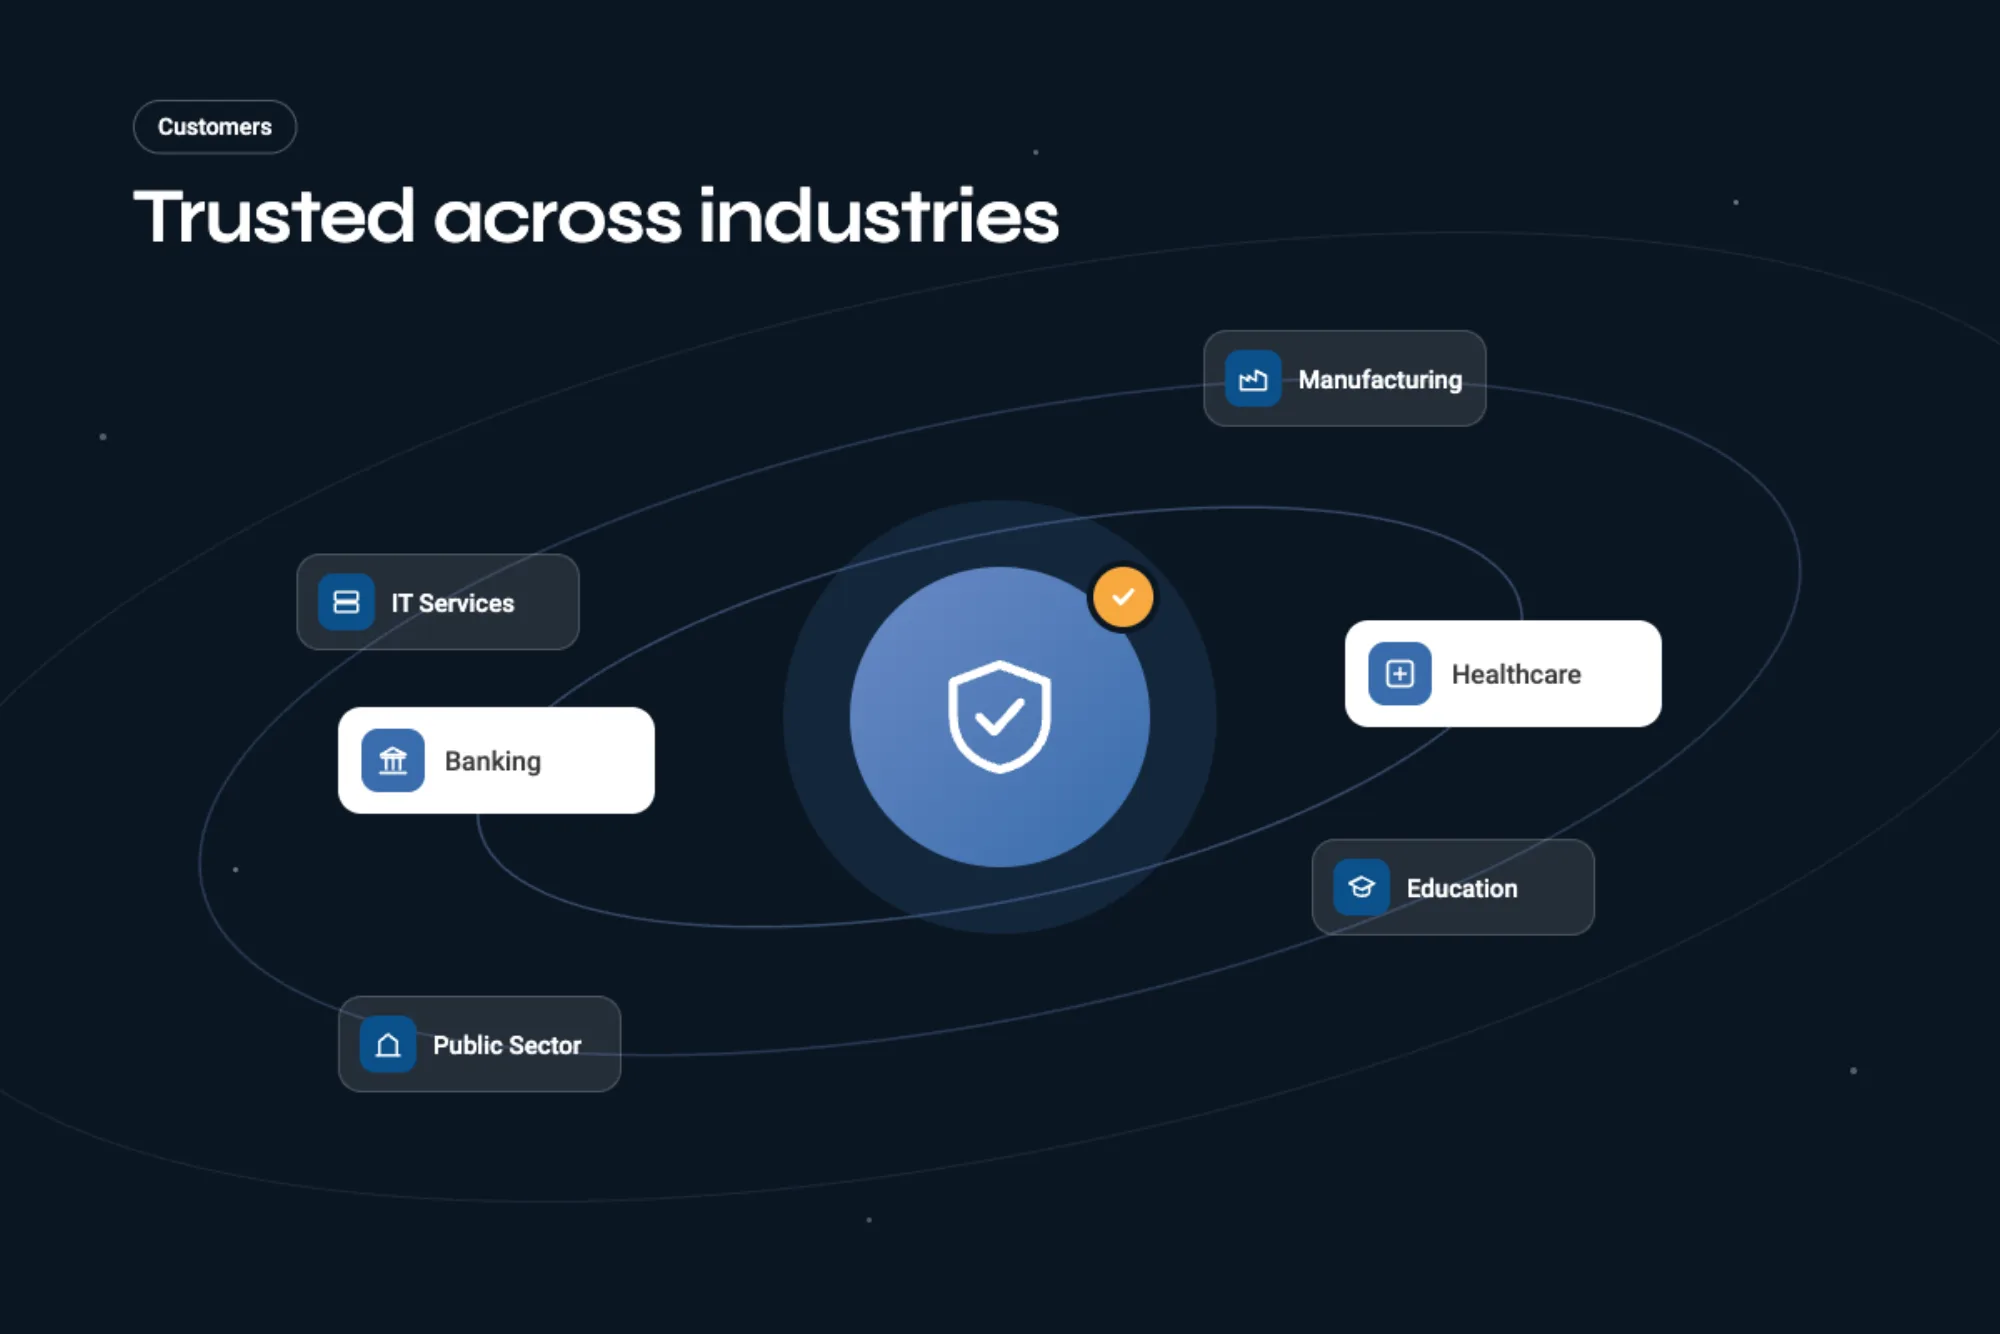
1,000+ organizations. Here is what changed.
Hospitals, banks, manufacturers and public bodies that had the same question you have: who can reach this data, and what happens the night somebody encrypts it.

Syslog CEF and REST, into the tool you already run
In their own words
Five customers on what changed.
None of them set out to buy a data security platform. They set out to answer a question an auditor, a board or an attacker had already asked them. Pick one.
“Without these solutions, I would feel less comfortable.”
OLVG, one of Amsterdam’s oldest and largest hospitals, needed to secure sensitive patient data and keep critical systems available for thousands of staff and patients. Real-time monitoring, instant failover and anti-ransomware defense turned that exposure into something the IT team can sleep through.
Watch the film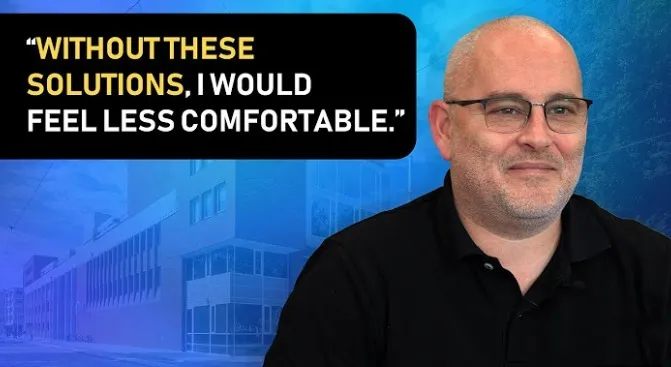
Protecting the data as close to the storage as it lives.
TFE uses ProLion to harden its file data against ransomware, to see what is actually happening to its files, and to secure the file environment itself. The film runs six minutes and is spoken in French.
Watch the film
“Products from ProLion are very user-friendly, and the data quality is stable.”
R-IT runs data centers for the Raiffeisen sector from Vienna, with around 1,000 staff across Austria, Slovakia and Slovenia. Measuring and billing a client’s storage used to mean a custom script and a database query every time, with no standard report to fall back on. ProLion turned that into reporting they can run, and cut the time it takes by 70 percent.
“I am really happy that these two containers have been set up here today at such impressive speed. This is the decisive step for the modernization and digitalization of our hospital. It couldn’t have gone any better.”
Klinikum Peine had no space for a redundant data center and no cheap way to build one. CANCOM delivered two high-security containers with a synchro-mirrored NetApp All-Flash MetroCluster across four active nodes, replicating to a third server room. ProLion monitoring sits on top of it: real-time detection and blocking of ransomware on the data itself, without agents on the clients.
“Thanks to the completely automatic intervention of the ClusterLion, downtime, a lot of remediation work, data loss, and a lot of working hours for the storage team were prevented.”
On a Sunday in spring 2022 an air-conditioning unit failed in one of the server rooms at the University of Bonn. The temperature rose until the room shut off its own electricity, taking the NetApp MetroCluster with it. ProLion saw the power go and started the failover to the second data center within seconds, so nothing went offline. It also held the affected cluster down until the room was repaired, which prevented a premature reboot.
Every story, by industry and storage.
What they tell us changed.
The question gets answered
Not “who is in the group” but “who can actually open this folder”, through every nested group, per file.
The restore gets smaller
The exact list of files one account touched, restored from the last clean snapshot, instead of a full-volume rollback.
The audit gets shorter
Evidence produced from the record rather than assembled by hand the week before.
Nothing leaves the building
Including at the sites that have no outbound connection at all, which is usually the reason we were called.
Talk to an engineer who knows your data.
Four fields, and somebody who knows ONTAP, PowerScale and what FPolicy does. Not a qualification call.