


Ransomware is a serious risk, with businesses being attacked every few seconds. Every day, hackers infiltrate a company’s systems and demand millions of dollars to return the data. One key sign that you’ve been hit by ransomware is the change in your file names. Suddenly, they get a new extension that wasn’t there before.
This article will walk you through what ransomware extensions mean, how they can help you identify the ransomware, and most importantly, how you can defend your organization.
What Are Ransomware Extensions?
Ransomware extensions are unique suffixes added to the names of encrypted files.
When ransomware infects your organization’s system, it encrypts your files, making them inaccessible. And then it modifies the file names by adding specific extensions.
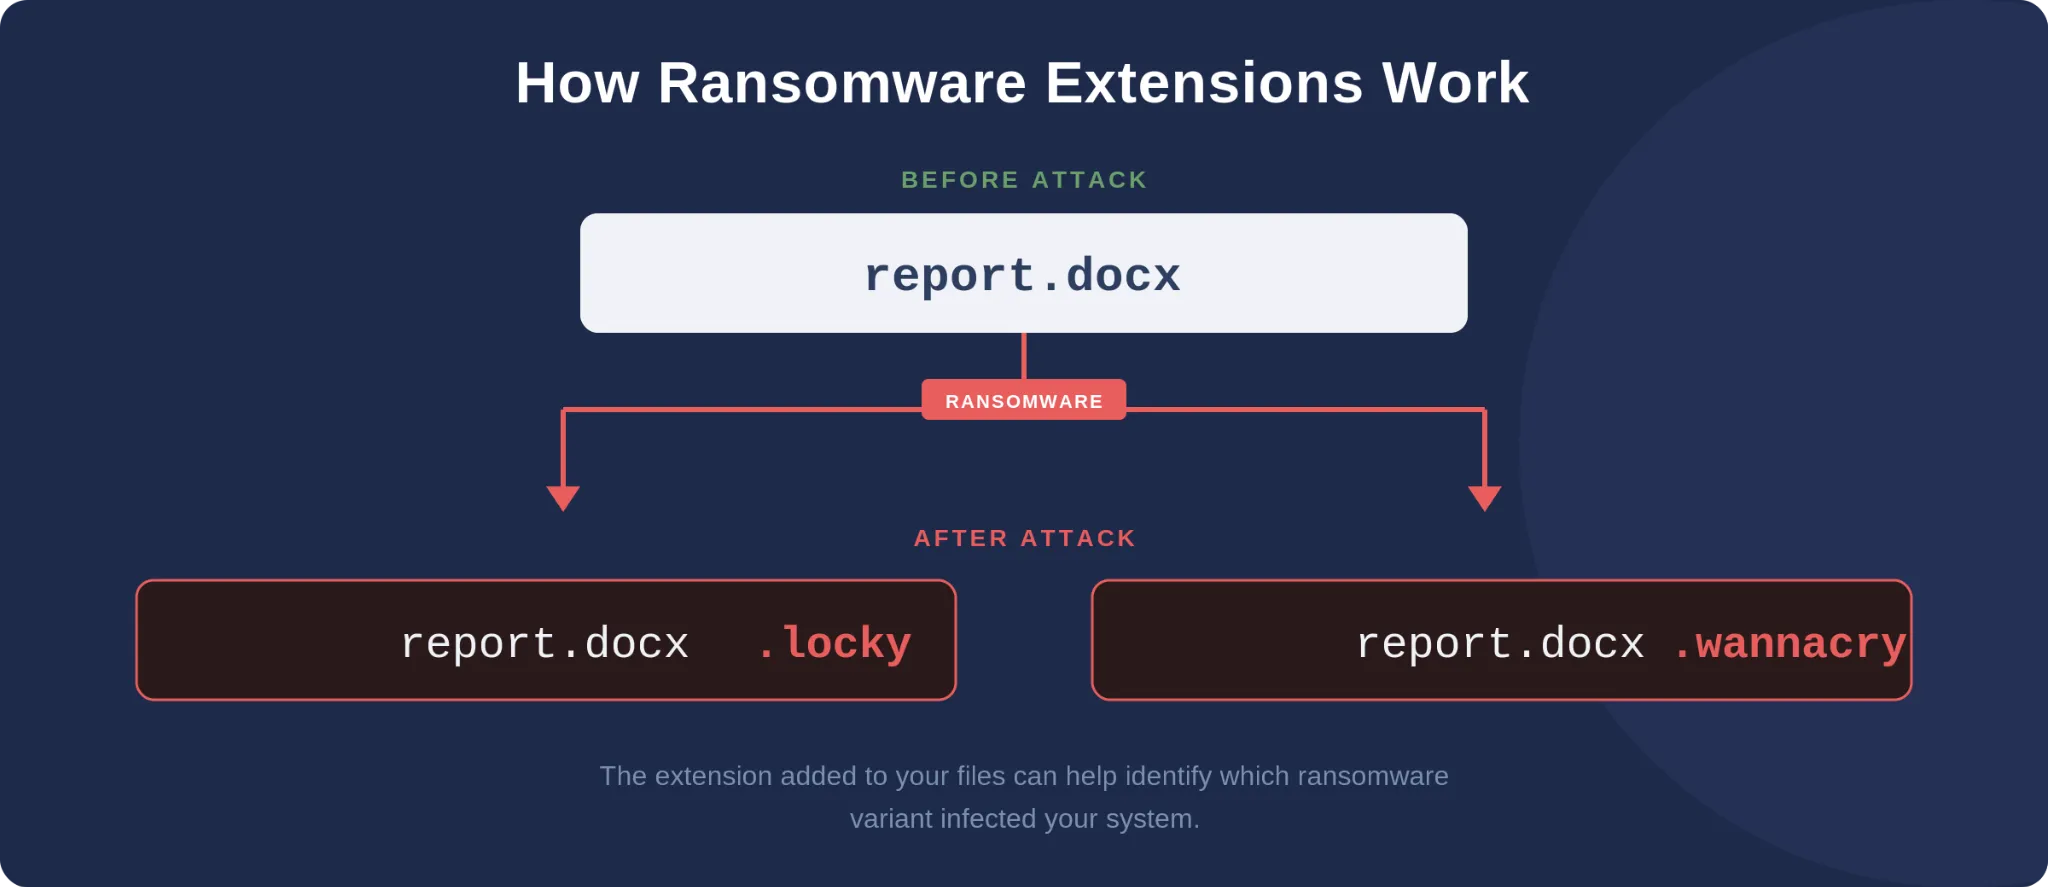
For instance, if you had a file named “quarterly_report.docx”, a ransomware attack might change it to “quarterly_report.docx.locky” or “quarterly_report.docx.wannacry,” depending on the type of ransomware.
What Do Ransomware Extensions Mean?
Ransomware extensions are a clear indicator that your files have been compromised. A bit like a cybercriminal’s signature, the extension can sometimes hint at the ransomware variant responsible for the attack. This information helps cybersecurity professionals identify the malware.
For example, a .locky extension points to the Locky ransomware.
What Are Some Common Ransomware Extensions? (Updated for 2026)
Some of the most notorious extensions come from well-known strains like .wannacry, .locky, and .badrabbit. However, there are many more.
Here are some of the most common ransomware extensions and what they mean. If your system has already been infected, you can use this list to recognize which type of ransomware you’re dealing with.
Tip: This list includes both historically significant ransomware strains and the most active variants in 2026.
- .qilin: Qilin was the most prolific ransomware group in 2025, responsible for over 1,000 attacks across healthcare, manufacturing, and finance
- .akira: The second most active group in 2025, Akira targets Windows, Linux, and ESXi environments and has grown rapidly through affiliate recruitment
- .dragonforce: DragonForce ransomware was behind some of the most high-profile attacks of 2025, including the breaches at Marks & Spencer and the Co-operative Group in the UK
- .play:Also known as Playcrypt, Play ransomware compromised approximately 900 organizations by mid-2025 using double extortion tactics
- .interlock: The Interlock group was responsible for the DaVita healthcare breach in 2025, which exposed the data of 2.7 million patients
- .lockbit: Despite law enforcement disruption in 2024, LockBit resurfaced with version 5.0 in late 2025 and remains a significant threat
- .clop or .cl0p: Cl0p returned to prominence in early 2025 by exploiting zero-day vulnerabilities in file transfer platforms, claiming over 390 victims in a single campaign
- .medusa: Medusa ransomware has targeted healthcare, education, and government organizations and was linked to attacks on major US institutions in 2025
Historically significant strains:
- .wannacry: WannaCry is known for its rapid global spread in 2017 and significant impact across multiple sectors
- .locky: Locky ransomware was famous for its aggressive encryption strategy and mass email distribution
- .cryptolocker: CryptoLocker, one of the first widely known ransomware strains, paved the way for the modern ransomware ecosystem
- .petya: Petya ransomware encrypts entire disk partitions, making it particularly destructive
- .notpetya or .nopetya: A more virulent derivative of Petya, NotPetya caused billions in damages globally in 2017
- .ryuk: Ryuk targeted large organizations and demanded ransom in cryptocurrency, later evolving into Conti
- .dharma: Dharma (also known as CrySiS) has continued to evolve over the years, using extensions like .dharma, .wallet, and .java
- .phobos: Phobos ransomware is known for its rapid encryption speed and has used extensions like .phobos, .deimos, and .epic
- .djvu: A variant of the STOP ransomware family, highly active in encrypting personal data
No longer active but historically notable:
- .conti: Conti ransomware targeted healthcare organizations and government agencies before the group dissolved in 2022
- .avaddon: Avaddon spread through phishing campaigns before the group shut down and released its decryption keys in 2021
- .egregor: Egregor targeted corporations with customized ransom notes before being disrupted by law enforcement in 2021
- .badrabbit: Bad Rabbit was known for targeted attacks, primarily in Russia and Eastern Europe, in 2017
Why Do Attackers Use Ransomware Extensions?
Extensions do more than just signal a successful attack, they are part of the cybercriminal’s psychological game.
By clearly marking which files have been encrypted, they remind the victim of what they stand to lose unless they pay up. This alteration of files adds to the urgency and fear, pushing individuals or companies towards considering the ransom payment.
Not All Ransomware Attacks Change Your File Extensions
It’s worth noting that not all modern ransomware attacks involve encryption. A growing number of groups are skipping encryption entirely and focusing on stealing data for extortion. In January 2026, the group WorldLeaks claimed to have stolen 1.4TB of data from Nike without encrypting a single file. They simply took the data and threatened to leak it.
In these cases, there won’t be any extension changes to spot, which is why monitoring for signs of a ransomware attack beyond file extensions is critical. Unusual outbound data transfers, unexpected access patterns, and changes to backup infrastructure can all signal an attack in progress, even when your file names look perfectly normal.
What Should You Do If You Notice Ransomware Extensions?
Discovering ransomware extensions on your files can be alarming, as it signals that your data has been compromised. It’s crucial to act promptly to mitigate the damage and begin the recovery process.
It’s important to understand that simply removing or changing the extension back to its original state won’t unlock your files. The encryption used in these attacks is sophisticated and can only be undone with a unique decryption key, which the attackers hold, or with specialized decryption tools.
If your system has been infiltrated by ransomware, you should consult your organization’s incident response plan to decide the next steps. Here are the steps that you will generally need to carry out after an attack:
- Disconnect from the Source: Immediately isolate the compromised device or server by disconnecting it from your network. This helps prevent the spread of the ransomware to other devices and systems. However, be sure to avoid destroying any data that will be important for forensics.
- Assess the Situation: With the immediate threat contained, identify the ransomware variant you’re dealing with and consider your next steps and available tools. Your incident response plan should outline the contingency measures you can take to mitigate the damage.
- Communicate with Leadership: Inform all relevant departments and stakeholders, including leadership, legal, PR, and HR, to coordinate your internal and external communication strategy.
- Determine Your Response Strategy: Carefully consider your options. It’s usually not a good idea to pay the ransom because it encourages attackers to strike again. And there’s no guarantee they will return your data. Instead, your incident response plan should include all relevant stakeholders, departments, and any potential third parties (such as forensic investigators and incident response retainers). This will help you find out which area of business has been exploited and put in processes and policies to eliminate the threat.
- Restore Data and Patch Up Vulnerabilities: Recover affected files and investigate the breach’s entry point to prevent future incidents.
Prevention Is the Best Defense Against Ransomware Extensions
Don’t wait until you see ransomware extensions in your network. Prevention is the best form of ransomware protection. And these days, it’s not a question of if attackers will strike, but when. So it’s essential to be prepared.
ProLion’s DataDefense automatically blocks ransomware extensions to prevent malicious software from infecting your system. It also identifies suspicious behavior and prevents the hacker from accessing your network. And with ProLion DataGovernance, you get the right tools to assess your current data.
In the unlikely event an attack is successful, ProLion can help you restore the specific files you need. Single-file restoration is faster and more reliable than traditional backups and can help you get back on track right away.
To learn more about how you can protect your organization from ransomware attacks, read the beginner’s guide to ransomware or get in touch with our team.
Frequently Asked Questions
Can you decrypt files with ransomware extensions?
It depends on the ransomware variant. Most modern ransomware uses strong encryption that can’t be reversed without the attacker’s unique decryption key.
How do I know which ransomware infected my system?
The file extension added to your encrypted files is often the fastest clue. Cross-referencing the extension against known ransomware strains (like the list in this article) can help you identify the variant. You can also check the ransom note, which usually contains the group’s name or contact information.
Can ransomware encrypt files without changing extensions?
Yes. Some ransomware variants encrypt file contents without modifying the file name or extension, making the attack harder to detect through file monitoring alone. And increasingly, some groups skip encryption entirely and focus on stealing data for extortion. This is why relying solely on extension changes as a detection method isn’t enough.