



Ransomware groups are increasingly targeting your vendors, partners, and software supply chain. That means even if your cybersecurity strategy is solid, your organization is still vulnerable.
In this article, we’ll break down how ransomware supply chain attacks work, explore recent examples like Whole Foods and FC Barcelona, and share proactive steps you can take to reduce your risk.
What Are Ransomware Supply Chain Attacks?
Ransomware supply chain attacks target the weaker links in your vendor, supplier, or service provider network. Instead of attacking your company directly, cybercriminals breach a trusted third party to gain indirect access or wreak havoc in your operations.
This tactic allows them to compromise multiple organizations at once, and could cost the global economy $138 billion by 2031.
Risks of Ransomware Supply Chain Attacks
A ransomware attack on one of your suppliers can quickly become your problem. Today’s supply chains are deeply interconnected. When one link breaks, the ripple effect can hit businesses across the network.
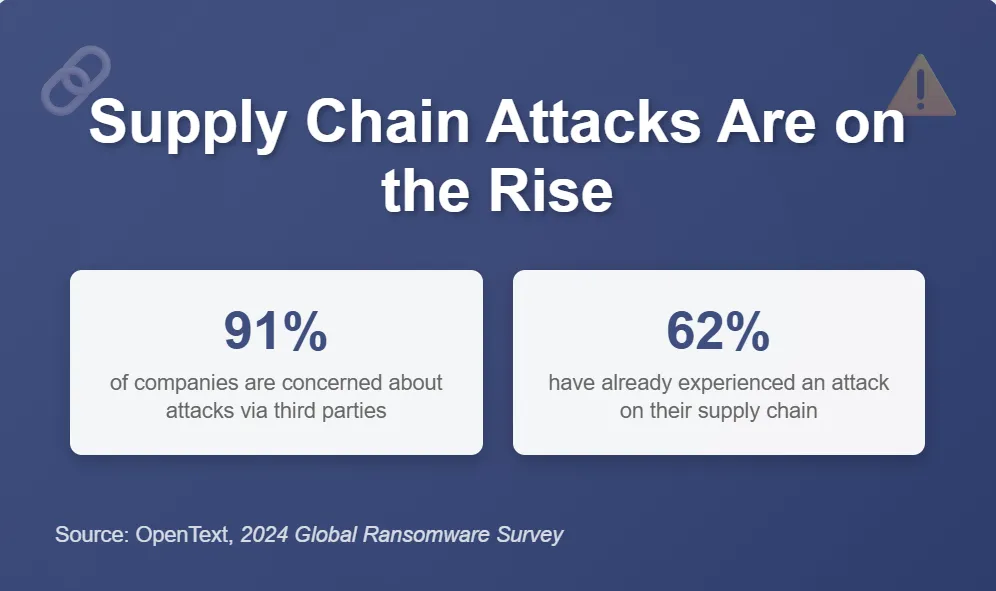
According to recent research, 91% of companies are concerned about ransomware attacks via third parties, and 62% have already experienced one.
A supply chain attack can lead to:
- Operational Disruptions: A ransomware attack can disrupt manufacturing, logistics, shipping, billing, customer service, and any other part of your operations
- Data Breach: Third-party vendors often have access to your business’s sensitive data, like customer information, confidential business data, and employee details
- Reputational Damage: Association with a breached supplier can damage your brand’s reputation, especially if your brand is more well-known than theirs
- Regulatory and Legal Issues: If the breach results in the loss of personal data, your business could face regulatory fines and legal challenges
- Financial Loss: The costs to recover from the attack and the impact of production delays and lost sales can be significant
Examples of Ransomware Supply Chain Attacks in 2025
Let’s take a look at some ransomware attacks on third-party vendors, why they happened, and the business impact on their partners.
FC Barcelona & Asefa
In June 2025, a ransomware group targeted Asefa, the Madrid-based subsidiary of French insurer SMABTP, and stole over 200GB of sensitive data. Among the leaked files was confidential information about high-profile clients, including FC Barcelona. The result? FC Barcelona made the headlines for all the wrong reasons.
Whole Foods & United Natural Foods Inc.
In June 2025, United Natural Foods Inc. (UNFI), the primary supplier for Whole Foods, suffered a ransomware attack that disrupted grocery deliveries across North America. Whole Foods shoppers encountered empty shelves, and the company stated that the incident would negatively impact their quarterly income.
Swiss Government & Radix
A Swiss health nonprofit, Radix, was hit by ransomware criminals who stole and encrypted their data, then published 1.3TB of files on the dark web. The breach exposed sensitive government data since Radix works with various Swiss federal offices, prompting the national cybersecurity center to investigate.
How to Prevent Ransomware Attacks on Your Supply Chain
Here are some best practices to secure your organization against third-party attacks:
- Develop a Comprehensive Third-Party Inventory
Start by mapping out all vendors within your supply chain to identify potential vulnerabilities. Remember, sometimes the smallest partners can pose the largest risks if their security measures are not up to scratch.
- Prioritize Security in Vendor Selection
When companies choose new partners, cybersecurity is often an after-thought. You need to ensure their security practices align with your standards and that they can demonstrate a strong commitment to cybersecurity.
- Conduct Regular Assessments and Insist on Transparency
Perform assessments during onboarding and on an on-going basis to monitor risk. Partners should be transparent about their cybersecurity practices.
If you don’t have your own assessment, ProLion’s cybersecurity resilience assessment is a good place to start. It flags your (or your partner’s) vulnerabilities and gives you tailored recommendations for improvement.
- Set Clear Data Handling Policies
Establish and enforce strict guidelines for data storage and transfer to prevent unauthorized access or breaches. Ensuring that vendors treat your data with the utmost security minimizes risks to your information.
- Enforce the Principle of Least Privilege
Principle of least privilege means employees and vendors only have the minimum level of access necessary for their tasks, which limits the damage in the event of an attack.
The most effective way to monitor user and file access permissions is with DataGovernance from ProLion. You can set up regular reports to keep an eye on who has access to what, and adjust if necessary.
- Plan a Containment Strategy
It’s important to plan ahead so you are prepared if one of your partners is attacked.
If they have access to your IT environment, you will need to be able to isolate and block their access. DataDefense from ProLion detects unusual activities in your file system and immediately blocks suspicious users.
And if the hackers manage to encrypt your files, you can restore the files you need using the granular restore function.
Secure Your Supply Chain Before Ransomware Strikes
Start by assessing your third-party risk and closing the gaps in your defenses. ProLion’s tools help you monitor access, detect threats in real time, and stay a step ahead of attackers. Book a demo or take the assessment to find out how well-prepared you are to defend your organization against attacks.


